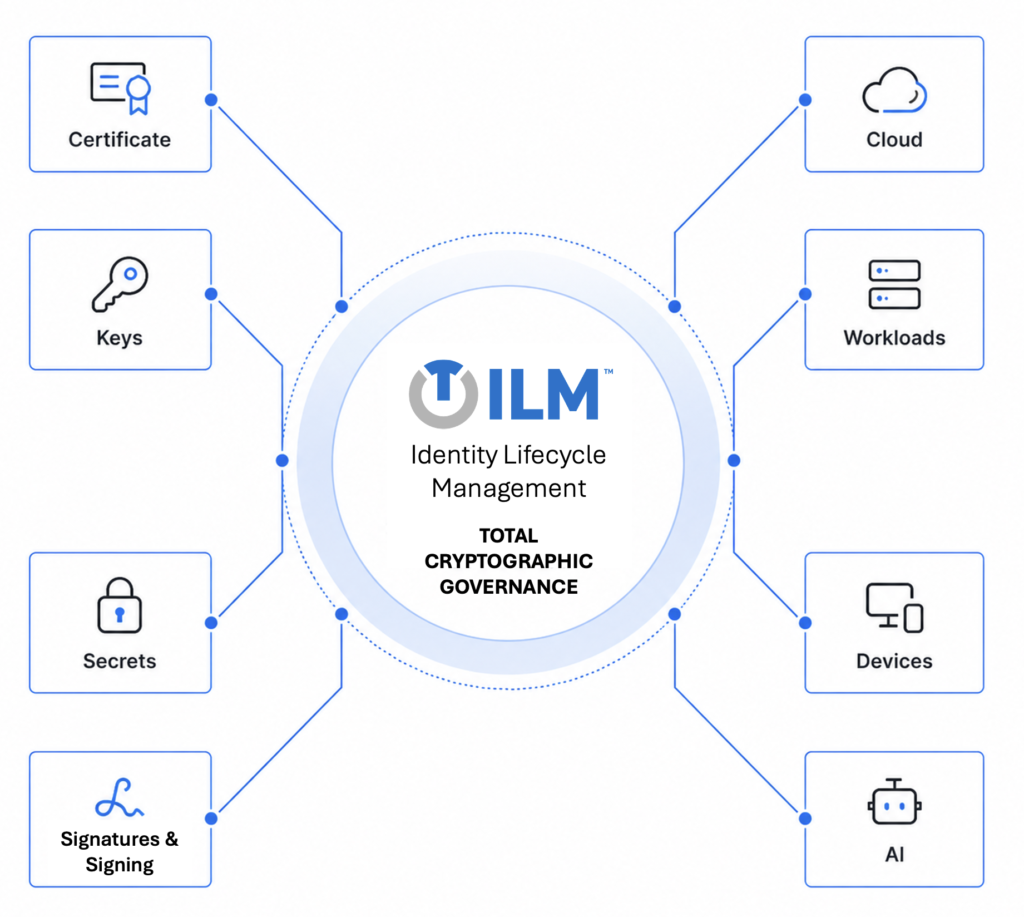
Identity Lifecycle Management (ILM) unifies fragmented cryptographic assets across cloud, applications, devices, workloads, and AI into one control plane. It extends traditional CLM beyond certificate renewal and outage prevention to deliver enterprise-wide cryptographic lifecycle governance.
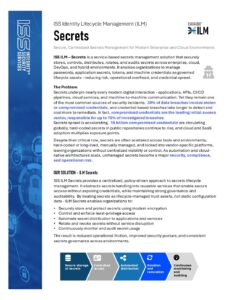
Centralizes secure storage and lifecycle management for passwords, application secrets, tokens, and machine credentials across enterprise, cloud, and DevOps environments.
Enforces policy-driven access control with least-privilege authentication and separation of duties for users, applications, and services.
Automates secure distribution, rotation, and revocation of secrets without exposing credentials or disrupting operations.
Provides continuous monitoring, audit logging, and visibility to support compliance, incident response, and operational assurance.
Establish governed identities across systems and users with automated certificate and credential controls. Improve security posture and reduce manual operations.
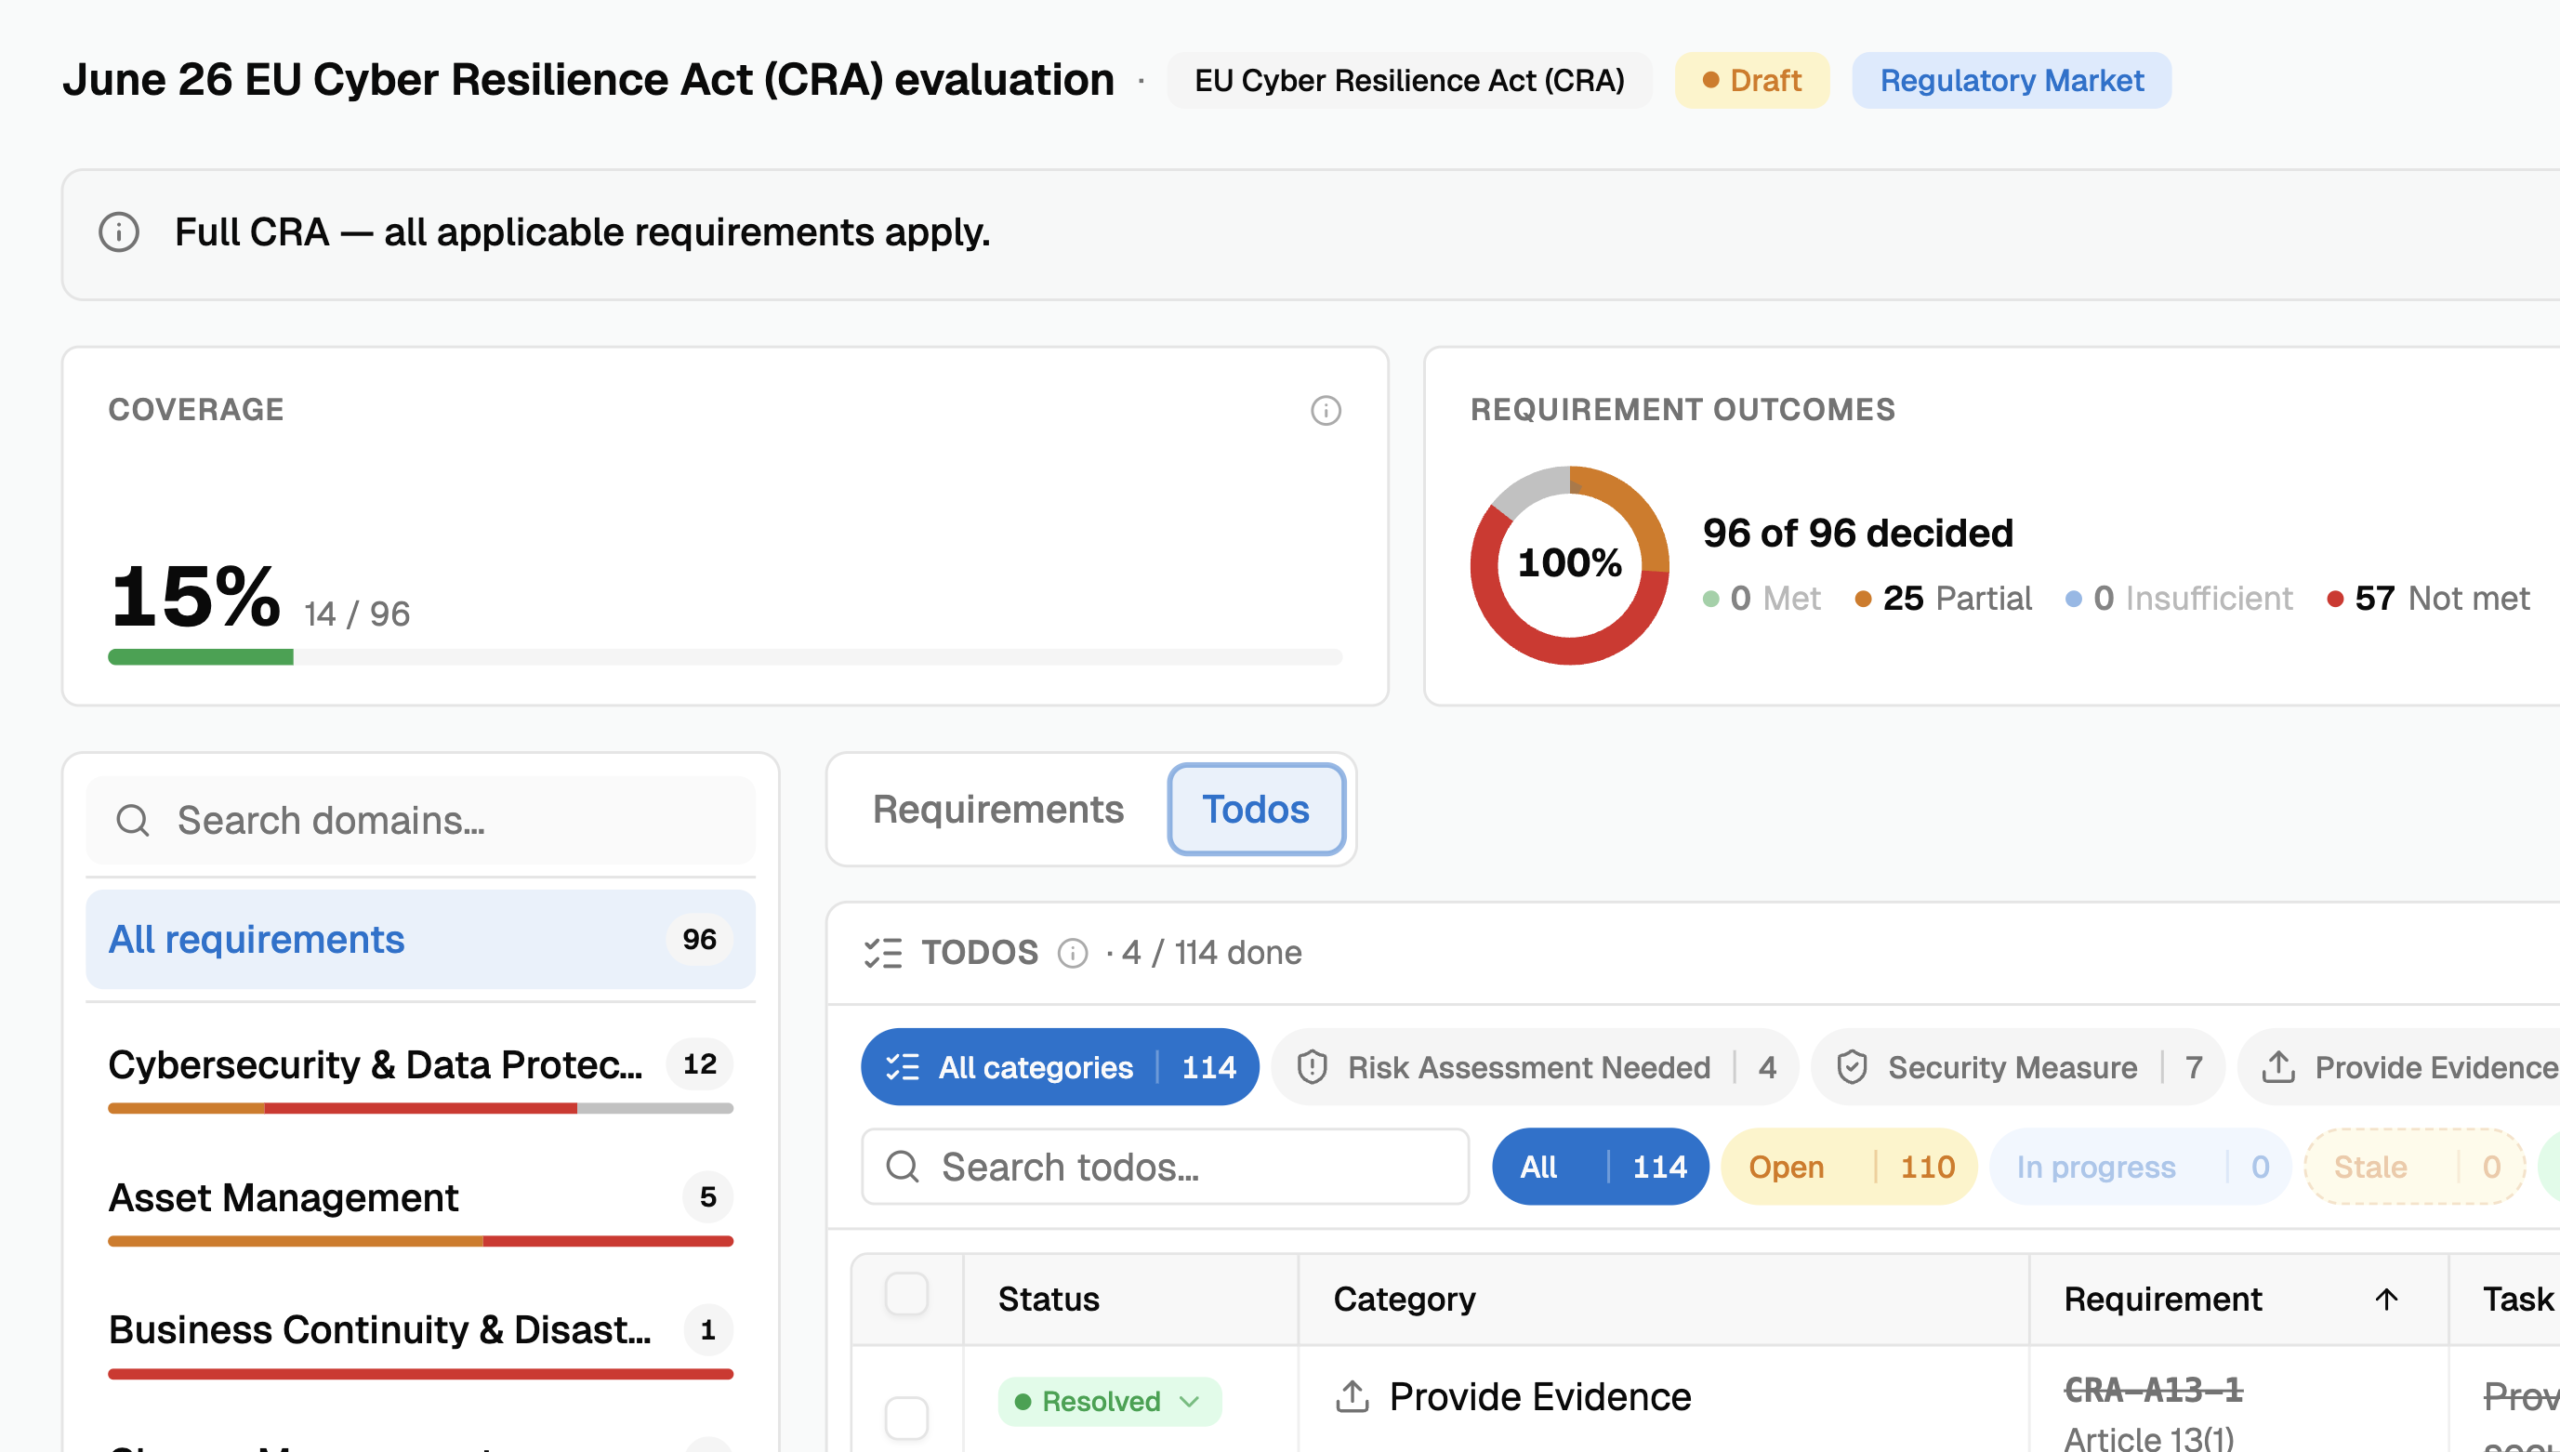
Assess & maintain continuous cyber trust across applications and infrastructure, with policy enforcement and audit-ready identity controls. Support evolving regulatory and industry requirements.
Modernize cryptography for the post-quantum era — with full discovery, assessment, and migration readiness.
Prepare for future cryptographic standards with managed certificate and key transitions. Enable secure hybrid algorithms without disrupting core business operations.
Flex applies to any industry that depends on embedded, IoT, or connected devices and infrastructure. Wherever devices must operate safely and securely, Flex delivers runtime trust and resilience. Selected industries where Flex is in high demand include:
A national public sector authority responsible for land registries, geodetic control, and core geographic data systems operates mission-critical platforms that support land ownership, infrastructure planning, and public administration across multiple regions.