📣 Integrity Security Services (ISS) is now OmniTrust.
Read our CEO’s Letter ->
+

OmniTrust and Entrust combine lifecycle automation with certified hardware protection and high-assurance digital signing to secure critical keys, certificates, and signing identities—reducing risk, strengthening compliance, and enabling cryptographic change without disruption.

Solution Focus

Hardware-Backed Key Protection Hardware-Backed Key Protection PKI Modernization & Machine Identity PKI Modernization & Machine Identity High-Assurance Digital Signing High-Assurance Digital Signing Post-Quantum & Crypto Agility Readiness Post-Quantum & Crypto Agility Readiness

OmniTrust + Entrust Joint Solution

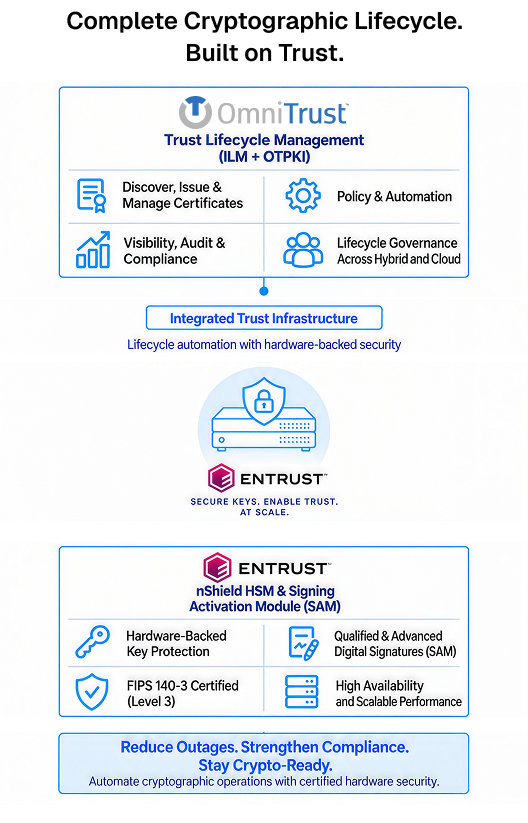
OmniTrust and Entrust combine lifecycle governance and automation with hardware-rooted cryptographic security to help organizations protect and manage trust across complex enterprise environments. Entrust nShield HSMs provide certified hardware-based protection for critical cryptographic keys and signing operations, while OmniTrust Trust Lifecycle Management provides centralized visibility, policy, and lifecycle automation across certificates, keys, and other cryptographic assets.

Together, the technologies establish hardware-rooted trust while simplifying how cryptographic assets are discovered, issued, renewed, revoked, and governed across hybrid and multi-cloud environments. The joint solution supports enterprise PKI and certificate lifecycle management, trusted digital signing, and HSM-backed key protection—helping reduce operational risk and strengthen auditability.

Joint customers gain a unified lifecycle view of cryptographic assets, automated certificate operations that reduce outage risk, and stronger auditability for requirements including eIDAS, NIS2, and DORA. The combined solution also supports crypto-agility and the transition toward post-quantum cryptography without disrupting critical operations.

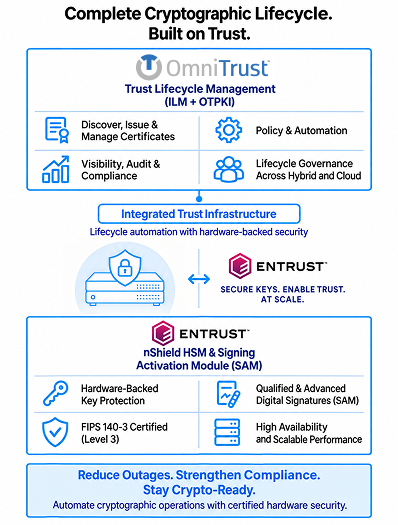
Joint solution diagram

Joint Customer Solution

Entrust OmniTrust Joint Customer Value
ILM PKI
Entrust nShield HSMs (nShield 5c, nShield 5s) Provides a certified hardware root of trust (FIPS 140-3 Level 3, EN 419221-5) for CA, signing, and encryption keys, combined with centralized lifecycle governance and automation across cryptographic assets.
Entrust Signing Activation Module (SAM) with nShield Enables remote qualified and advanced electronic signatures with sole control for eIDAS trust services, combined with lifecycle governance of certificates, keys, and signing identities.
Entrust Cryptographic Security Platform (PKI, Key Management Vault, Compliance Manager with KeySafe) Extends lifecycle governance and visibility across Entrust-protected cryptographic assets, helping organizations simplify certificate and key operations, strengthen compliance, and maintain crypto-agility.

Entrust nShield HSMs (nShield 5c, nShield 5s)

ILM
Supported
PKI
Supported
Joint Customer Value
Provides a certified hardware root of trust (FIPS 140-3 Level 3, EN 419221-5) for CA, signing, and encryption keys, combined with centralized lifecycle governance and automation across cryptographic assets.

Entrust Signing Activation Module (SAM) with nShield

ILM
Supported
PKI
Not supported
Joint Customer Value
Enables remote qualified and advanced electronic signatures with sole control for eIDAS trust services, combined with lifecycle governance of certificates, keys, and signing identities.

Entrust Cryptographic Security Platform (PKI, Key Management Vault, Compliance Manager with KeySafe)

ILM
Supported
PKI
Supported
Joint Customer Value
Extends lifecycle governance and visibility across Entrust-protected cryptographic assets, helping organizations simplify certificate and key operations, strengthen compliance, and maintain crypto-agility.

Solution Use Cases

Trusted Digital Signing & Cryptographic Lifecycle Management

Challenge:

Trust service providers and regulated enterprises need to issue certificates and create trusted digital signatures while meeting stringent security and regulatory requirements. Signing keys must remain protected in certified hardware, certificate lifecycles must be efficiently managed, and cryptographic operations must remain auditable as organizations prepare for evolving requirements and post-quantum cryptography.

Solution:

Entrust nShield HSMs and the Entrust Signing Activation Module provide certified hardware-based key protection and secure remote signature activation. Combined with OmniTrust Identity Lifecycle Management, organizations can govern certificates, keys, and signing identities across their lifecycle, automate certificate operations, and maintain centralized visibility across the cryptographic environment.

Customer Benefit:

Organizations can deliver trusted digital signing services with hardware-rooted key protection, reduce certificate-related outages and operational complexity, strengthen auditability for regulatory requirements including eIDAS, NIS2, and DORA, and establish a controlled path toward post-quantum cryptography.

Enterprise PKI & Certificate Lifecycle Management

Challenge:

Enterprises must manage growing certificate estates across hybrid and multi-cloud environments while protecting critical CA keys and avoiding certificate-related outages. Manual processes and fragmented visibility increase operational risk and make it harder to maintain consistent governance.

Solution:

Entrust nShield HSMs provide certified hardware-based protection for critical CA and private keys, while OmniTrust ILM and OmniTrust PKI provide certificate lifecycle management, centralized visibility, policy, and automation across the environment.

Customer Benefit:

Organizations can protect critical PKI infrastructure while automating certificate discovery, issuance, renewal, and revocation—reducing outage risk, simplifying operations, and strengthening governance and auditability across their certificate estate.

Post-Quantum Readiness & Crypto-Agility

Challenge:

Organizations need to prepare for evolving cryptographic requirements and post-quantum algorithms without disrupting critical applications and services. Limited visibility into certificates, keys, and cryptographic dependencies can make migration planning complex and increase operational risk.

Solution:

Entrust provides hardware-rooted protection for critical cryptographic keys, while OmniTrust provides centralized visibility, lifecycle governance, and automation across cryptographic assets. The combined solution helps organizations identify and manage cryptographic dependencies as algorithms, certificates, keys, and policies evolve.

Customer Benefit:

Organizations gain greater visibility and control over their cryptographic environment, enabling them to plan and execute cryptographic changes more efficiently, reduce migration risk, and establish a controlled path toward post-quantum cryptography.

Resources

About Our Partner

Entrust secures people, devices, and data with identity-centric security. The company supports critical stages of the identity lifecycle, from verifying identity at onboarding, to securing connections and transactions, to protecting the keys, secrets, and certificates that underpin them. Its portfolio covers hardware security modules (HSM), public key infrastructure, certificate and key lifecycle management, identity verification, identity and access management, digital signing, and secure credential issuance. The Entrust nShield HSM family provides a certified hardware root of trust for cryptographic keys and signing operations. Entrust supports customers in more than 150 countries through a global partner network, and works with regulated sectors including financial services, government, telecommunications, energy, and trust service providers. Its solutions are designed for crypto-agility and post-quantum readiness, so customers can plan cryptographic change without disrupting operations.

https://www.entrust.com Headquarters 1187 Park Place, Shakopee, Minnesota 55379, United States

Ready to learn more?

Contact OmniTrust to discuss how the OmniTrust + Entrust joint solution can help your organization.

Contact Us