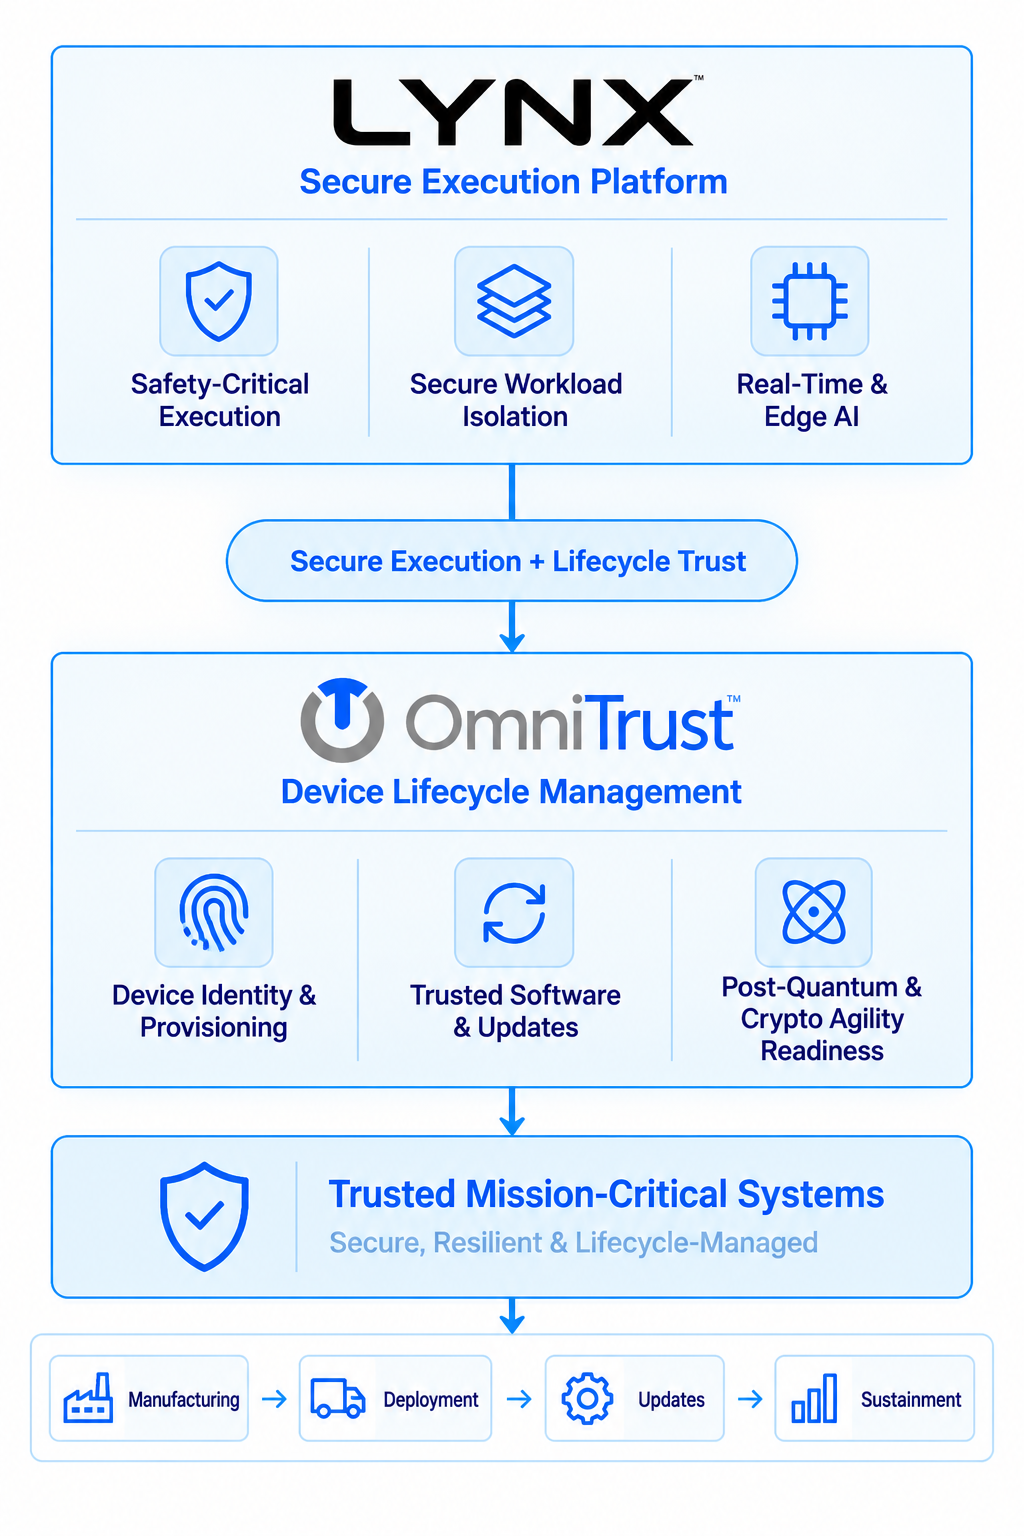
OmniTrust and Lynx bring together secure execution environments and device lifecycle trust to protect safety-critical systems across OT, aerospace, and defense. Lynx provides deterministic real-time performance, secure partitioning, and isolation of mixed-criticality workloads, enabling traditional mission applications, graphics, and AI capabilities to operate within controlled environments. OmniTrust Device Lifecycle Management (DLM) complements these capabilities with hardware-rooted device identity, secure manufacturing and provisioning, software and firmware signing, integrity verification, trusted updates, and cryptographic lifecycle management.
The technologies work together by combining Lynx’s protected execution and workload isolation with OmniTrust’s ability to establish device trust, verify software integrity, and securely manage updates throughout the system lifecycle. This helps ensure that trusted software is deployed and maintained within secure, isolated execution environments, even as applications and mission requirements evolve.
Together, these complementary capabilities support a continuous chain of trust from initial provisioning through deployment, maintenance, and long-term sustainment. This helps OT, aerospace, and defense organizations securely introduce new capabilities, protect against unauthorized software changes, and maintain operational resilience across decades of service, while supporting cryptographic agility and post-quantum cryptography (PQC) readiness as security requirements evolve.

 Safety-Critical Execution
 Secure Workload Isolation
 Real-Time & Edge AI
 Device Identity & Provisioning
 Trusted Software & Updates
 Post-Quantum & Crypto Agility Readiness